A subscriber walks into a building with no coverage and connects to Wi-Fi. For calls and messaging to keep working, that untrusted Wi-Fi has to reach your core over a secure tunnel, and the subscriber's SIM has to be authenticated against the HSS. The Ouroboros ePDG terminates the tunnel; the colocated AAA authenticates the SIM. The same product becomes the N3IWF of your 5G core.
VoWiFi lets subscribers make calls and send messages over any Wi-Fi network: home broadband, a café, an airport. None of those networks are under operator control. They are, by definition, untrusted access.
The problem is bridging that untrusted access to the EPC and IMS core without exposing either. The Wi-Fi leg has to be encrypted end to end into the operator network, and the subscriber's identity has to be verified against the HSS using the SIM credentials — not a username and password. Without a gateway that terminates a secure tunnel and an authenticator that speaks SIM-based EAP, VoWiFi either does not work or is not safe to turn on.
For an MVNO there is a second problem, and it is financial. Every VoLTE call, video call, or SMS a subscriber makes is carried by the host MNO — national or roaming — and has to be compensated at that host's wholesale data rate. A session originated or terminated over VoWiFi never touches the host network, so that cost is zero. Every minute moved onto Wi-Fi is margin the MVNO keeps, and room to price against operators who own their own radio.
ePDG and AAA in one network element
The Ouroboros ePDG and AAA are collocated in a single network element. IPsec/IKEv2 termination, EAP authentication and the Diameter client toward the HSS run together, with direct access to the authentication vectors and session state shared in memory. The external interfaces stay standard: SWu toward the handset, SWx toward the HSS, S2b toward the PGW. The AAA can also serve a third-party ePDG or Wi-Fi access over SWm, STa and SWa.
The ePDG terminates the IPsec tunnel and connects the subscriber to the PGW over S2b
The handset discovers the ePDG through DNS and builds an IPsec tunnel to it over IKEv2, one tunnel per PDN connection. The ePDG connects each tunnel to the PGW over S2b, placing the subscriber's session into the same EPC bearer path used by LTE — so the IMS core sees a VoWiFi session the same way it sees a VoLTE one. The Ouroboros ePDG works with the Ouroboros PDN-GW, PCRF and OCS, or with those of other vendors.
The AAA authenticates the SIM against the HSS — no separate password
During tunnel set-up, the AAA authenticates the subscriber with EAP-AKA or EAP-AKA', with the vectors of the HSS over SWx, or EAP-SIM with an HLR over MAP Gr. EAP-AKA' is supported end to end: the Ouroboros HSS derives CK' and IK', the AAA checks the AT_MAC and derives the keys. Devices without a SIM are served by the integrated captive portal.
Emergency calls, handover and the 5G core
Emergency calls over Wi-Fi reach a dedicated emergency PDN with priority QoS, and can be accepted with limited or no authentication where regulation requires it. Handover between VoWiFi and VoLTE works in both directions with the same IP address, anchored at the PGW. In a 5G Standalone core, the same product runs as the N3IWF: EAP-5G toward the AMF, one IPsec child SA per PDU session toward the UPF.
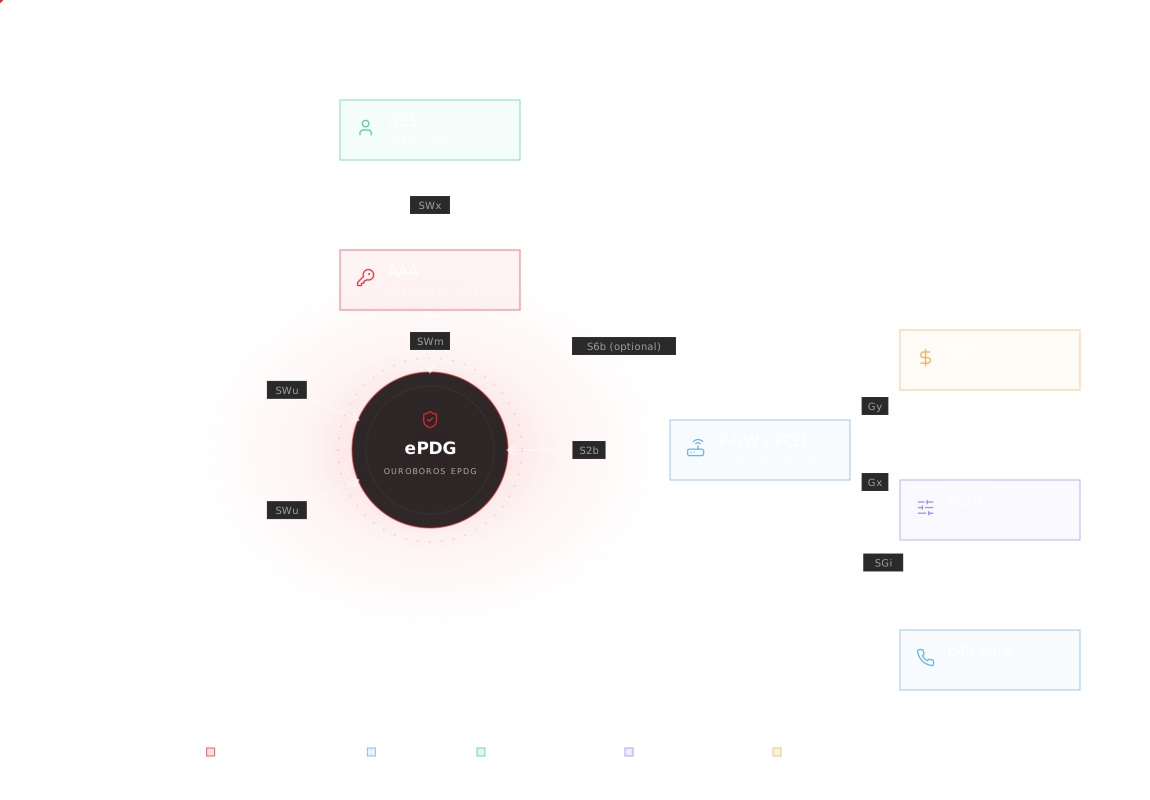
ePDG · AAA — untrusted Wi-Fi access into the EPC
Coverage extension, Wi-Fi roaming, emergency calls, seamless handover, 5G — one access path for all VoWiFi scenarios.
VoWiFi coverage extension
Subscribers in buildings, basements, or rural areas with poor cellular coverage place calls over home or venue Wi-Fi. The ePDG tunnels the session into the EPC and the AAA authenticates the SIM, so the call uses the operator's IMS core with no change to the subscriber experience.
Roaming over Wi-Fi
A subscriber abroad connects to local Wi-Fi and reaches the home IMS core through the ePDG, authenticated by the AAA against the home HSS. This offers calling and messaging without cellular roaming charges, using the home network's services.
Emergency calls over Wi-Fi
A subscriber dials an emergency number while on Wi-Fi. The ePDG detects the emergency indication, connects the session to the emergency PDN with priority QoS, and the IMS routes the call to the emergency services.
VoWiFi / VoLTE handover continuity
A subscriber on a VoWiFi call walks out of Wi-Fi range onto the cellular network, or back. The session moves between the ePDG path and the LTE path without dropping the call.
Wi-Fi calling on the 5G core
Operators moving to 5G Standalone switch the same product to N3IWF mode, so Wi-Fi calling follows the subscribers to the 5G core.
We've selected Ouroboros because it was the best company capable of fulfilling our need for a scalable and virtualised full MVNO platform. Moreover, the Ouroboros team is pragmatic, flexible and responsive.
Pascal Prot
CEO-CTO · Legos
Collocated ePDG and AAA
One element for tunnel termination and authentication: fewer points of failure, less signalling between functions, lower latency at attach. An integrated AAA module also works with a standard third-party HSS.
EAP-AKA' end to end
The AAA supports EAP-AKA' with key derivation by the HSS, as well as EAP-AKA and EAP-SIM. Authentication meets current 3GPP security requirements for non-3GPP access.
SIM-less devices
Tablets, laptops and connected objects without a SIM authenticate through the integrated captive portal.
Emergency attach
Dedicated emergency PDN, priority QoS, and limited or unauthenticated access for emergency calls where regulation requires it.
VoWiFi / VoLTE handover
An active session moves between the Wi-Fi and cellular paths in both directions without dropping, with the same IP address.
ePDG and N3IWF in one product
The same software runs as an ePDG for the 4G core or as an N3IWF for the 5G core. VoWiFi works over both.
Detail records
Connection records (accepted or rejected) are written as CSV files for billing, statistics and troubleshooting.
IPv4, IPv6 and dual-stack
Subscribers get IPv4, IPv6 or both addresses per session, and the gateway runs over IPv4 or IPv6 networks. Operators moving to IPv6 need no separate configuration path.
VoWiFi turns every Wi-Fi network into coverage — but only if the untrusted access leg is secured and the subscriber is authenticated by their SIM. The Ouroboros ePDG and AAA do both in one element: one terminates the tunnel, the other authenticates against the HSS, with no AAA interworking to integrate.
They reuse the existing EPC and IMS core rather than duplicating it, mix with other vendors' PGW, OCS and PCRF, and move to the 5G core as an N3IWF without a new product. Several ePDGs can be stacked behind the same or different PGWs as traffic grows.

Tell us your EPC and HSS vendors and your VoWiFi plans, and we'll confirm how the ePDG and AAA fit between the Wi-Fi access leg and your existing core.
 Product datasheet
4G / LTE · 4G/LTE
ePDG & AAA — VoWiFi Access Gateway
A subscriber walks into a building with no coverage and connects to Wi-Fi. For calls and messaging to keep working, that untrusted Wi-Fi has to reach your core over a secure tunnel, and the subscriber's SIM has to be authenticated against the HSS. The Ouroboros ePDG terminates the tunnel; the colocated AAA authenticates the SIM. The same product becomes the N3IWF of your 5G core.
In production since 2025 · 148M+ subscribers · 99.999% availability
Untrusted access on one side, wholesale cost on the other
VoWiFi lets subscribers make calls and send messages over any Wi-Fi network: home broadband, a café, an airport. None of those networks are under operator control. They are, by definition, untrusted access.
The problem is bridging that untrusted access to the EPC and IMS core without exposing either. The Wi-Fi leg has to be encrypted end to end into the operator network, and the subscriber's identity has to be verified against the HSS using the SIM credentials — not a username and password. Without a gateway that terminates a secure tunnel and an authenticator that speaks SIM-based EAP, VoWiFi either does not work or is not safe to turn on.
For an MVNO there is a second problem, and it is financial. Every VoLTE call, video call, or SMS a subscriber makes is carried by the host MNO — national or roaming — and has to be compensated at that host's wholesale data rate. A session originated or terminated over VoWiFi never touches the host network, so that cost is zero. Every minute moved onto Wi-Fi is margin the MVNO keeps, and room to price against operators who own their own radio.
Untrusted Wi-Fi, securely tunnelled into the core.
ePDG and AAA in one network element
The Ouroboros ePDG and AAA are collocated in a single network element. IPsec/IKEv2 termination, EAP authentication and the Diameter client toward the HSS run together, with direct access to the authentication vectors and session state shared in memory. The external interfaces stay standard: SWu toward the handset, SWx toward the HSS, S2b toward the PGW. The AAA can also serve a third-party ePDG or Wi-Fi access over SWm, STa and SWa.
The ePDG terminates the IPsec tunnel and connects the subscriber to the PGW over S2b
The handset discovers the ePDG through DNS and builds an IPsec tunnel to it over IKEv2, one tunnel per PDN connection. The ePDG connects each tunnel to the PGW over S2b, placing the subscriber's session into the same EPC bearer path used by LTE — so the IMS core sees a VoWiFi session the same way it sees a VoLTE one. The Ouroboros ePDG works with the Ouroboros PDN-GW, PCRF and OCS, or with those of other vendors.
The AAA authenticates the SIM against the HSS — no separate password
During tunnel set-up, the AAA authenticates the subscriber with EAP-AKA or EAP-AKA', with the vectors of the HSS over SWx, or EAP-SIM with an HLR over MAP Gr. EAP-AKA' is supported end to end: the Ouroboros HSS derives CK' and IK', the AAA checks the AT_MAC and derives the keys. Devices without a SIM are served by the integrated captive portal.
Emergency calls, handover and the 5G core
Emergency calls over Wi-Fi reach a dedicated emergency PDN with priority QoS, and can be accepted with limited or no authentication where regulation requires it. Handover between VoWiFi and VoLTE works in both directions with the same IP address, anchored at the PGW. In a 5G Standalone core, the same product runs as the N3IWF: EAP-5G toward the AMF, one IPsec child SA per PDU session toward the UPF.
ePDG · AAA — untrusted Wi-Fi access into the EPC
How operators use it.
Coverage extension, Wi-Fi roaming, emergency calls, seamless handover, 5G — one access path for all VoWiFi scenarios.
VoWiFi coverage extension
Subscribers in buildings, basements, or rural areas with poor cellular coverage place calls over home or venue Wi-Fi. The ePDG tunnels the session into the EPC and the AAA authenticates the SIM, so the call uses the operator's IMS core with no change to the subscriber experience.
Roaming over Wi-Fi
A subscriber abroad connects to local Wi-Fi and reaches the home IMS core through the ePDG, authenticated by the AAA against the home HSS. This offers calling and messaging without cellular roaming charges, using the home network's services.
Emergency calls over Wi-Fi
A subscriber dials an emergency number while on Wi-Fi. The ePDG detects the emergency indication, connects the session to the emergency PDN with priority QoS, and the IMS routes the call to the emergency services.
VoWiFi / VoLTE handover continuity
A subscriber on a VoWiFi call walks out of Wi-Fi range onto the cellular network, or back. The session moves between the ePDG path and the LTE path without dropping the call.
Wi-Fi calling on the 5G core
Operators moving to 5G Standalone switch the same product to N3IWF mode, so Wi-Fi calling follows the subscribers to the 5G core.
Specifications.
Inside the platform.
Collocated ePDG and AAA
One element for tunnel termination and authentication: fewer points of failure, less signalling between functions, lower latency at attach. An integrated AAA module also works with a standard third-party HSS.
EAP-AKA' end to end
The AAA supports EAP-AKA' with key derivation by the HSS, as well as EAP-AKA and EAP-SIM. Authentication meets current 3GPP security requirements for non-3GPP access.
SIM-less devices
Tablets, laptops and connected objects without a SIM authenticate through the integrated captive portal.
Emergency attach
Dedicated emergency PDN, priority QoS, and limited or unauthenticated access for emergency calls where regulation requires it.
VoWiFi / VoLTE handover
An active session moves between the Wi-Fi and cellular paths in both directions without dropping, with the same IP address.
ePDG and N3IWF in one product
The same software runs as an ePDG for the 4G core or as an N3IWF for the 5G core. VoWiFi works over both.
Detail records
Connection records (accepted or rejected) are written as CSV files for billing, statistics and troubleshooting.
IPv4, IPv6 and dual-stack
Subscribers get IPv4, IPv6 or both addresses per session, and the gateway runs over IPv4 or IPv6 networks. Operators moving to IPv6 need no separate configuration path.
VoWiFi turns every Wi-Fi network into coverage — but only if the untrusted access leg is secured and the subscriber is authenticated by their SIM. The Ouroboros ePDG and AAA do both in one element: one terminates the tunnel, the other authenticates against the HSS, with no AAA interworking to integrate.
They reuse the existing EPC and IMS core rather than duplicating it, mix with other vendors' PGW, OCS and PCRF, and move to the 5G core as an N3IWF without a new product. Several ePDGs can be stacked behind the same or different PGWs as traffic grows.
HSS
The AAA authenticates VoWiFi subscribers against the HSS over SWx. The same subscriber profile drives LTE and VoWiFi access.
PDN-GW
The ePDG connects to the PGW over S2b. VoWiFi sessions ride the same EPC bearer path as LTE.
N3IWF
The 5G mode of the same product: Wi-Fi access to the 5G SA core.
IMS Core
Voice and video calls over Wi-Fi.
Next step
Launching VoWiFi and need untrusted Wi-Fi access into your core?
Tell us your EPC and HSS vendors and your VoWiFi plans, and we'll confirm how the ePDG and AAA fit between the Wi-Fi access leg and your existing core.