- 01Virtualised Evolved Packet CorevEPC
- 02Home Subscriber ServerHSS
- 03Packet Data Network GatewayPDN-GW
- 04Diameter Routing AgentDRA
- 05Equipment Identity RegisterEIR
- 06Policy and Charging Rules FunctionPCRF
- 07Messaging CenterSMSC
- 08IP-SMS GatewayIP-SM-GW
- 09Gateway Mobile Location CentreGMLC
- 10IMS Core with TAS and MRFIMS
- 11Access Network Discovery and Selection FunctionANDSF
- 12Cell Broadcast CentreCBC
Part of the Registration center, encompassing HLR, HSS, EIR and 5G UDM/AUSF on one User Data Repository. Provision a subscriber once for 2G, 3G, 4G, IMS and 5G.
4G authentication runs over Diameter and SIP. 2G and 3G authentication runs over MAP by HLR. These are different protocols, which is why most standalone HSS deployments sit alongside an existing HLR as a separate system — separate database, separate provisioning workflow, and a synchronisation layer in between.
That synchronisation layer is the problem. A subscriber provisioned in the HLR needs to appear in the HSS before they can attach to LTE. When the sync is delayed or fails, the subscriber cannot authenticate. When a service profile changes, two records need updating. Every gap between the two systems is an operational cost and a potential source of authentication failures.
The Ouroboros HSS removes that layer: it shares one User Data Repository (UDR) with the HLR, the 5G UDM, the PCRF and the OCS, so there is only one point of provisioning.
Every LTE attach starts here
Every LTE authentication starts at the HSS. When a subscriber attaches to 4G, the MME queries the HSS over the S6a Diameter interface. The HSS validates the subscriber, returns authentication vectors, and provides the subscriber profile — QoS class, APN configuration, roaming permissions. Without it, no subscriber can attach to LTE.
One UDR, shared with the HLR
The Ouroboros HSS shares its User Data Repository directly with the HLR Front-End. A subscriber provisioned once is immediately visible to both 2G MAP-based authentication and 4G Diameter-based authentication. One record. One provisioning point. No synchronisation layer to build, maintain, or debug.
AuC, EIR, and HLR built in
The integrated 4G/5G AuC handles all LTE, IMS and 5G authentication flows. New ciphering algorithms deploy on demand without a hardware refresh. EIR (2G to 5G), HLR and the 5G UDM, AUSF and IMS services over the SBI are built in on the same UDR. Wi-Fi access through the ePDG or the N3IWF authenticates over SWx, SMS routing for the SMSC and IP-SM-GW runs over S6c, and location services over SLh. Each subscriber can carry multiple public and private identities, such as mobile handset, PDA, and connected device, consolidated to a single bill.
Multi-tenant, to tens of millions
Roaming profiles are configurable per Visited PLMN. Multi-tenant operation lets a single node host several MCC/MNC ranges. This is useful for MVNO operators or operators running more than one licence. Scales from 1 000 to over 50 million subscribers: millions of subscribers per node vertically, several tens of millions horizontally.
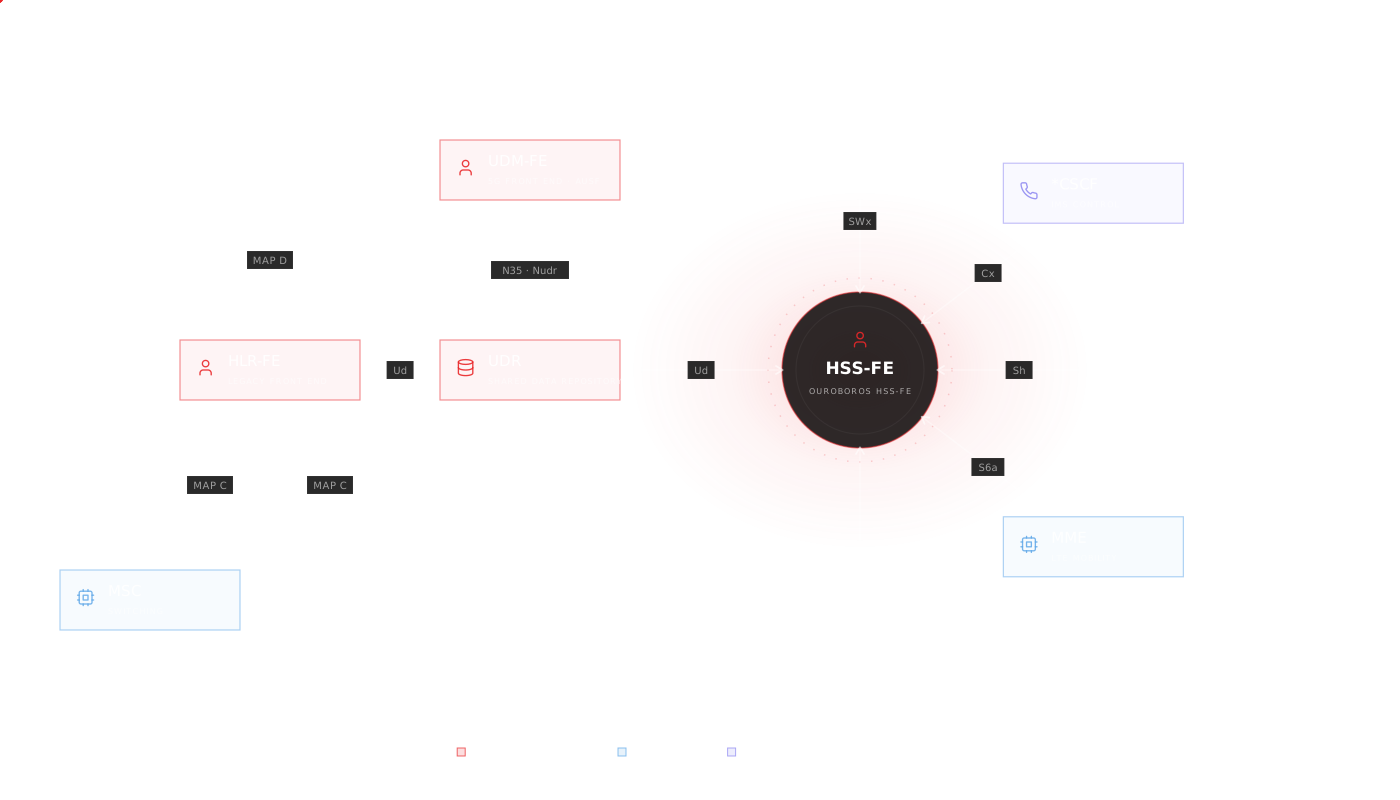
HSS-FE · shared UDR behind the legacy and LTE front ends
LTE alongside 2G, full-MVNO 4G, VoLTE, M2M fleets, national roaming — one subscriber core.
MNO deploying LTE alongside an existing 2G/3G network
The shared UDR means 4G authentication draws from the same subscriber record already in use for 2G. No migration. No parallel provisioning workflows. Subscribers move between generations transparently.
Operator building a full 4G platform
MNO, MNA, MVNOs who need full subscriber ownership, not dependence on the host MNO's HSS, provision their own subscribers with multi-tenant MCC/MNC hosting for third-party OSS/BSS integration.
IMS and VoLTE deployment
VoLTE authentication requires an IMS-aware HSS. The HSS handles SIP-based subscriber registration for IMS services. Multiple public IDs per subscriber cover voice, video, and messaging identities under one account.
M2M and IoT deployments
Connected devices authenticate against the same HSS as voice subscribers. The multi-identity model handles device fleets where one SIM represents multiple logical endpoints.
Multi-operator or national roaming
Per-VPLMN roaming profiles configure different service rules for each roaming partner. An operator managing national roaming agreements assigns correct QoS and service tier per partner automatically at attach.
We've selected Ouroboros because it was the best company capable of fulfilling our need for a scalable and virtualised full MVNO platform. Moreover, the Ouroboros team is pragmatic, flexible and responsive.
Pascal Prot
CEO-CTO · Legos
Shared UDR with HLR-FE and UDM
One data repository serves 2G MAP-based, 4G Diameter-based and 5G SBI-based authentication. Provision a subscriber once. Both generations see the same record immediately. No sync layer to maintain.
Integrated 4G AuC with on-demand ciphering
New authentication and ciphering algorithms activate without hardware replacement. Algorithm upgrades are configuration changes, not infrastructure projects.
Per-VPLMN roaming profiles
Each visited network carries distinct service rules, features, QoS parameters, and data plan restrictions. Roaming agreements enforce automatically at attach — no manual case-by-case handling.
Multi-identity per subscriber
A single account carries multiple IMSI or MSISDN across different device types, depending on their PLMN or SIM choice. The mobile is reachable by all its identities.
Multi-tenant MCC/MNC support
A single node hosts multiple operator identities simultaneously with several OP/OPc. MVNO operators and multi-licence operators share infrastructure without data separation risk.
3GPP standards evolution included
Compliance tracks 3GPP updates without additional licensing cost. Standards upgrades do not trigger a new procurement cycle.
EIR, HLR and 5G on the same repository
The EIR (2G to 5G), the HLR and the 5G UDM, AUSF and IMS services run on the same UDR. One subscriber and device database for the whole network, with sequence numbers shared across generations.
IPv4, IPv6 and dual-stack
Every interface runs over IPv4, IPv6 or both. The element fits an IPv6 core or a mixed network without a separate configuration.
The operational cost of running a separate HSS and HLR is the gap between them. Every provisioning error, every sync delay, every reconciliation failure between two databases is a cost that compounds as the subscriber base grows. The Ouroboros HSS removes that gap by design, holding subscriber data at the data model level rather than copying it between systems.
The HSS has been in production since 2015. It runs for operators including Airnity and Legos. Carrier-grade availability and 3GPP compliance are not claims here. They are a production record.
OPEX rental is available, starting at 1 000 subscribers. Cost scales with the network, not with what the network might become.

What HLR are you running today, and how many subscribers sit behind it? We'll show how the shared UDR removes the synchronisation layer and what deployment looks like on your timeline.
 Product datasheet
4G / LTE · 4G/LTE
Home Subscriber Server (HSS)
Part of the Registration center, encompassing HLR, HSS, EIR and 5G UDM/AUSF on one User Data Repository. Provision a subscriber once for 2G, 3G, 4G, IMS and 5G.
In production since 2015 · 148M+ subscribers · 99.999% availability
Two databases. One synchronisation problem.
4G authentication runs over Diameter and SIP. 2G and 3G authentication runs over MAP by HLR. These are different protocols, which is why most standalone HSS deployments sit alongside an existing HLR as a separate system — separate database, separate provisioning workflow, and a synchronisation layer in between.
That synchronisation layer is the problem. A subscriber provisioned in the HLR needs to appear in the HSS before they can attach to LTE. When the sync is delayed or fails, the subscriber cannot authenticate. When a service profile changes, two records need updating. Every gap between the two systems is an operational cost and a potential source of authentication failures.
The Ouroboros HSS removes that layer: it shares one User Data Repository (UDR) with the HLR, the 5G UDM, the PCRF and the OCS, so there is only one point of provisioning.
One record. Both generations. No sync layer.
Every LTE attach starts here
Every LTE authentication starts at the HSS. When a subscriber attaches to 4G, the MME queries the HSS over the S6a Diameter interface. The HSS validates the subscriber, returns authentication vectors, and provides the subscriber profile — QoS class, APN configuration, roaming permissions. Without it, no subscriber can attach to LTE.
One UDR, shared with the HLR
The Ouroboros HSS shares its User Data Repository directly with the HLR Front-End. A subscriber provisioned once is immediately visible to both 2G MAP-based authentication and 4G Diameter-based authentication. One record. One provisioning point. No synchronisation layer to build, maintain, or debug.
AuC, EIR, and HLR built in
The integrated 4G/5G AuC handles all LTE, IMS and 5G authentication flows. New ciphering algorithms deploy on demand without a hardware refresh. EIR (2G to 5G), HLR and the 5G UDM, AUSF and IMS services over the SBI are built in on the same UDR. Wi-Fi access through the ePDG or the N3IWF authenticates over SWx, SMS routing for the SMSC and IP-SM-GW runs over S6c, and location services over SLh. Each subscriber can carry multiple public and private identities, such as mobile handset, PDA, and connected device, consolidated to a single bill.
Multi-tenant, to tens of millions
Roaming profiles are configurable per Visited PLMN. Multi-tenant operation lets a single node host several MCC/MNC ranges. This is useful for MVNO operators or operators running more than one licence. Scales from 1 000 to over 50 million subscribers: millions of subscribers per node vertically, several tens of millions horizontally.
HSS-FE · shared UDR behind the legacy and LTE front ends
How operators use it.
LTE alongside 2G, full-MVNO 4G, VoLTE, M2M fleets, national roaming — one subscriber core.
MNO deploying LTE alongside an existing 2G/3G network
The shared UDR means 4G authentication draws from the same subscriber record already in use for 2G. No migration. No parallel provisioning workflows. Subscribers move between generations transparently.
Operator building a full 4G platform
MNO, MNA, MVNOs who need full subscriber ownership, not dependence on the host MNO's HSS, provision their own subscribers with multi-tenant MCC/MNC hosting for third-party OSS/BSS integration.
IMS and VoLTE deployment
VoLTE authentication requires an IMS-aware HSS. The HSS handles SIP-based subscriber registration for IMS services. Multiple public IDs per subscriber cover voice, video, and messaging identities under one account.
M2M and IoT deployments
Connected devices authenticate against the same HSS as voice subscribers. The multi-identity model handles device fleets where one SIM represents multiple logical endpoints.
Multi-operator or national roaming
Per-VPLMN roaming profiles configure different service rules for each roaming partner. An operator managing national roaming agreements assigns correct QoS and service tier per partner automatically at attach.
Specifications.
Inside the platform.
Shared UDR with HLR-FE and UDM
One data repository serves 2G MAP-based, 4G Diameter-based and 5G SBI-based authentication. Provision a subscriber once. Both generations see the same record immediately. No sync layer to maintain.
Integrated 4G AuC with on-demand ciphering
New authentication and ciphering algorithms activate without hardware replacement. Algorithm upgrades are configuration changes, not infrastructure projects.
Per-VPLMN roaming profiles
Each visited network carries distinct service rules, features, QoS parameters, and data plan restrictions. Roaming agreements enforce automatically at attach — no manual case-by-case handling.
Multi-identity per subscriber
A single account carries multiple IMSI or MSISDN across different device types, depending on their PLMN or SIM choice. The mobile is reachable by all its identities.
Multi-tenant MCC/MNC support
A single node hosts multiple operator identities simultaneously with several OP/OPc. MVNO operators and multi-licence operators share infrastructure without data separation risk.
3GPP standards evolution included
Compliance tracks 3GPP updates without additional licensing cost. Standards upgrades do not trigger a new procurement cycle.
EIR, HLR and 5G on the same repository
The EIR (2G to 5G), the HLR and the 5G UDM, AUSF and IMS services run on the same UDR. One subscriber and device database for the whole network, with sequence numbers shared across generations.
IPv4, IPv6 and dual-stack
Every interface runs over IPv4, IPv6 or both. The element fits an IPv6 core or a mixed network without a separate configuration.
The operational cost of running a separate HSS and HLR is the gap between them. Every provisioning error, every sync delay, every reconciliation failure between two databases is a cost that compounds as the subscriber base grows. The Ouroboros HSS removes that gap by design, holding subscriber data at the data model level rather than copying it between systems.
The HSS has been in production since 2015. It runs for operators including Airnity and Legos. Carrier-grade availability and 3GPP compliance are not claims here. They are a production record.
OPEX rental is available, starting at 1 000 subscribers. Cost scales with the network, not with what the network might become.
vEPC (MME/SGW/PGW)
The MME authenticates every LTE subscriber attach against the HSS over S6a. The two are designed to deploy together.
Home Location Register (HLR)
2G and 3G on the same UDR, with one provisioning point.
Unified Data Management (UDM)
5G SA subscriber data and AUSF on the same UDR.
DRA
All Diameter traffic between HSS, MME, PCRF, and OCS routes through the DRA. Reduces direct peer connections and centralises signalling control.
Next step
Deploying LTE alongside an existing 2G network?
What HLR are you running today, and how many subscribers sit behind it? We'll show how the shared UDR removes the synchronisation layer and what deployment looks like on your timeline.